Categories
 Sarees
 Women’s Wear
 Men's Wear
TOP RATED PRODUCTS
-
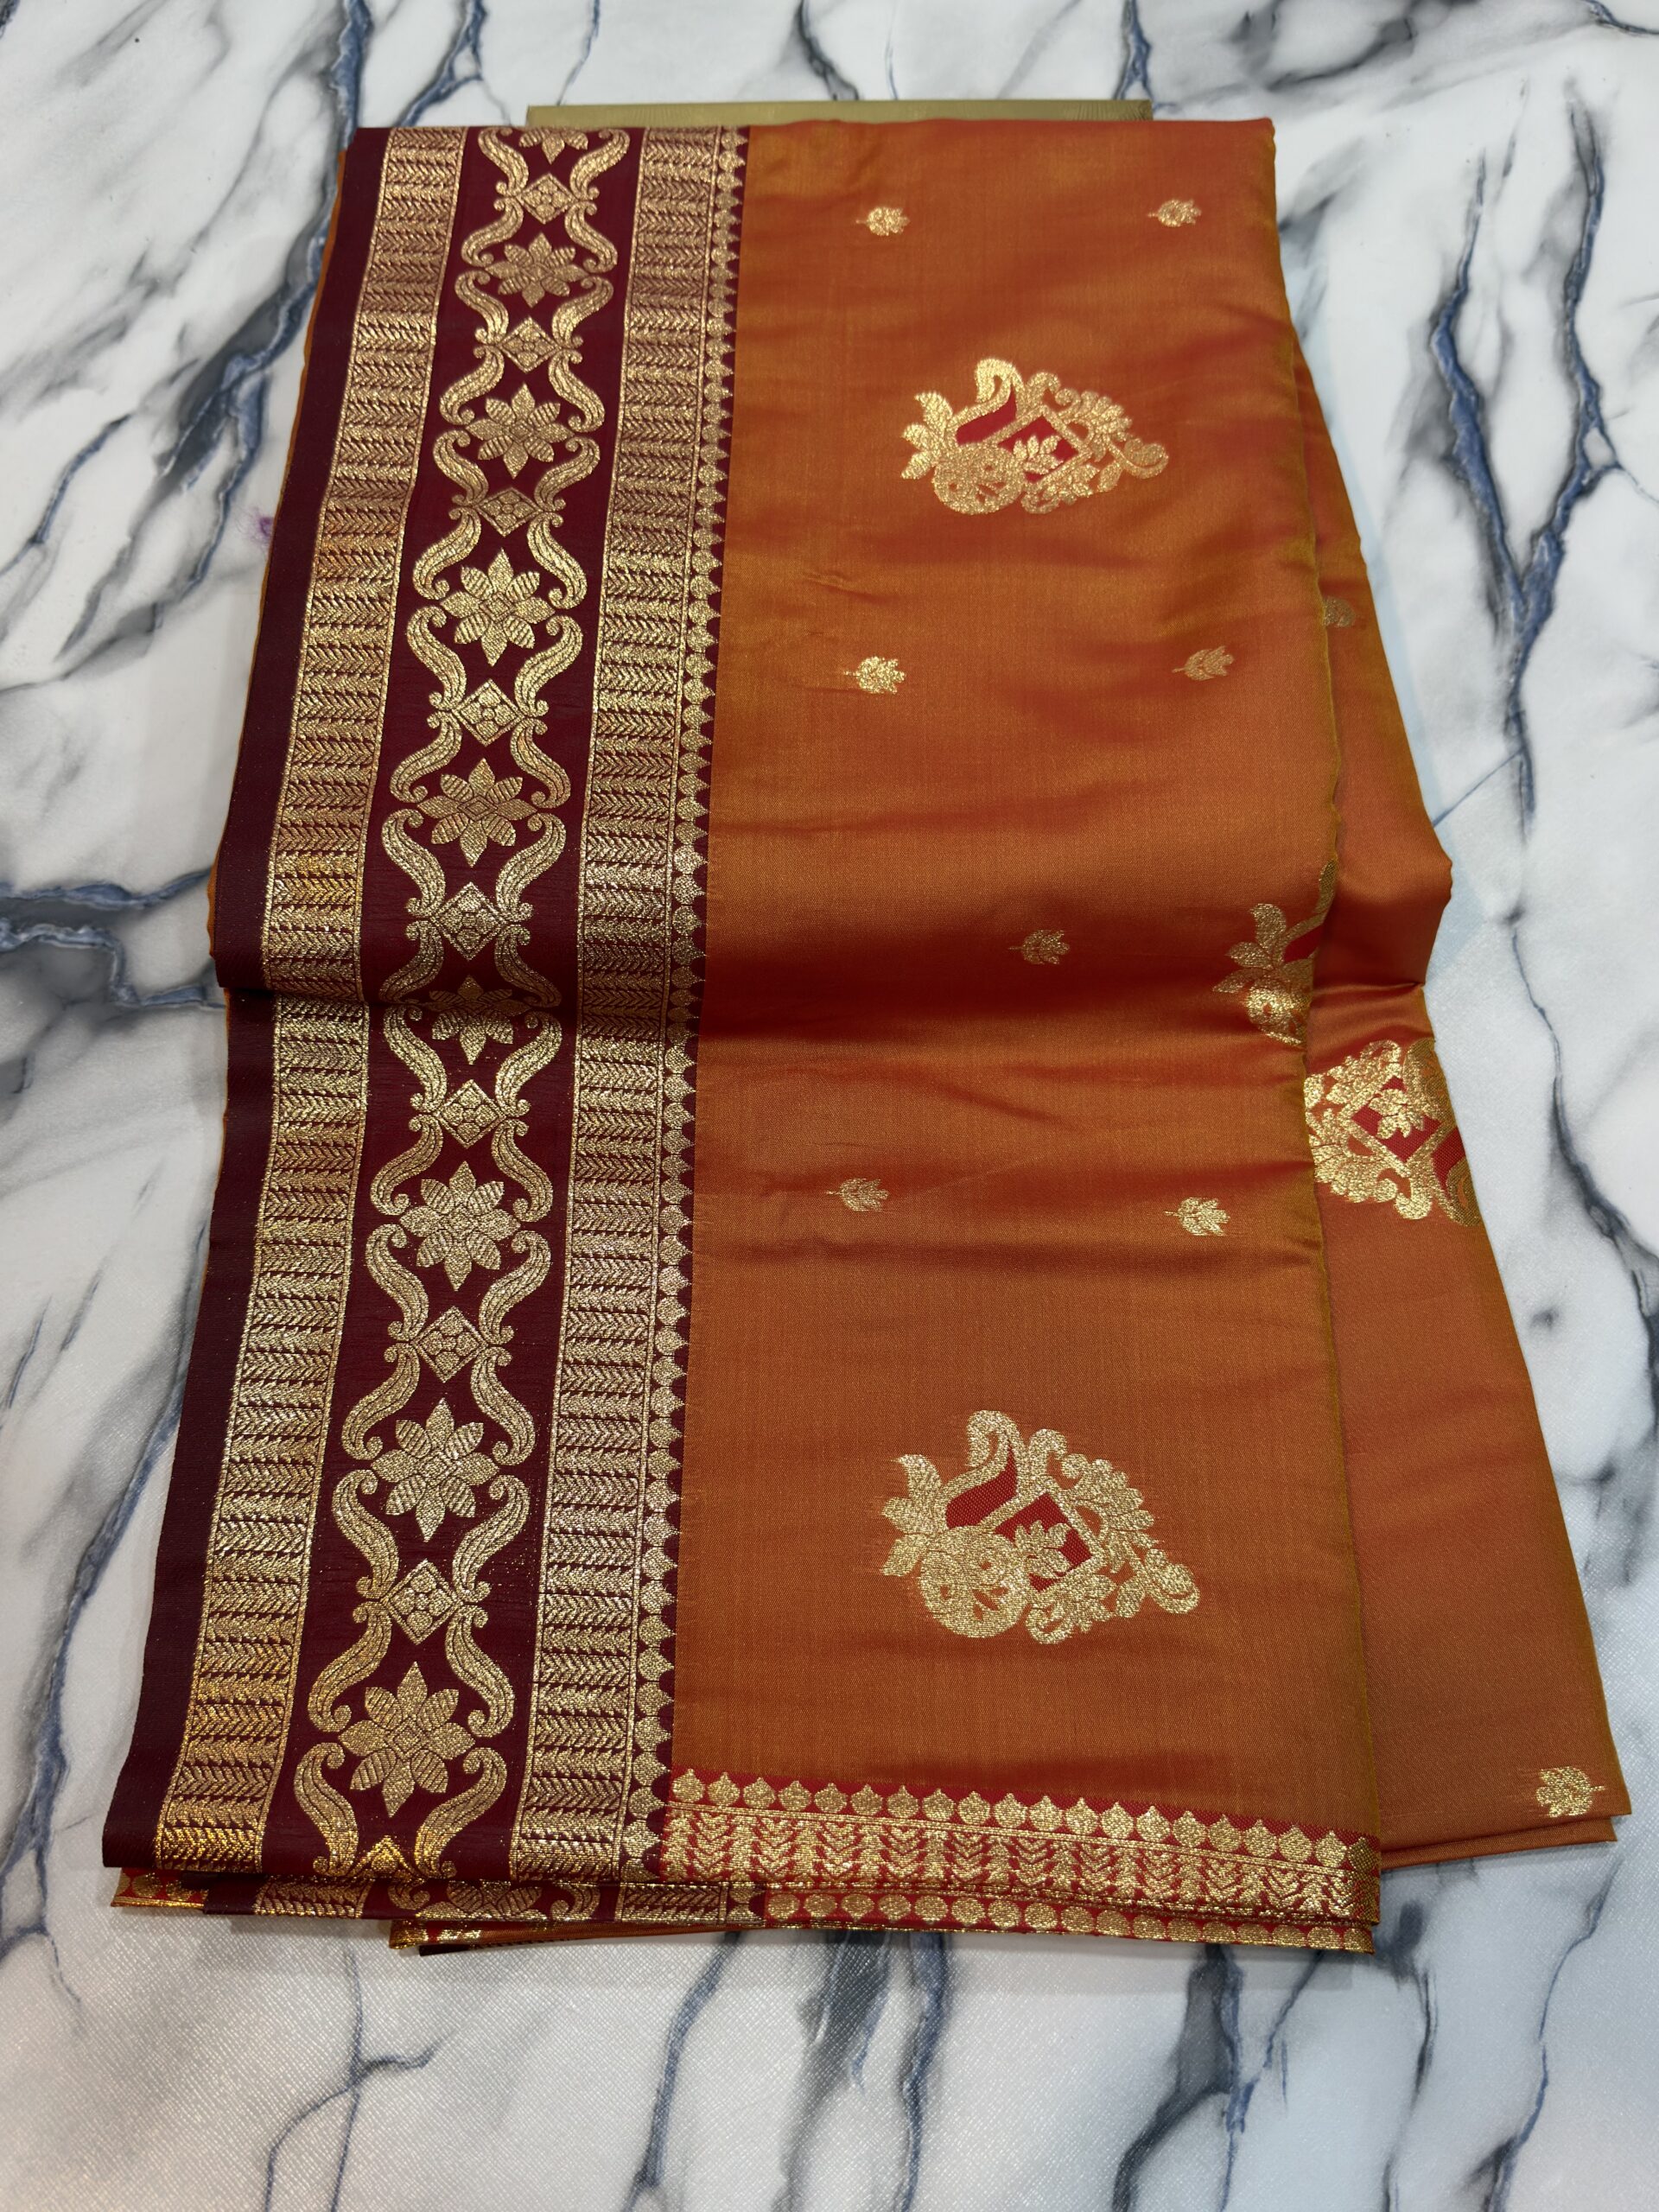
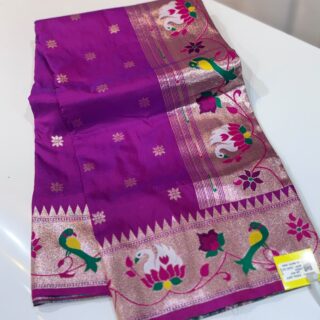 Rajhuns paithani #jh106
Original price was: ₹1,499.00.₹850.00Current price is: ₹850.00.
-
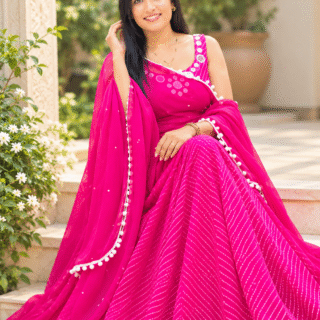 lehriya anarkali pattern #jh111
Original price was: ₹2,600.00.₹1,400.00Current price is: ₹1,400.00.
-
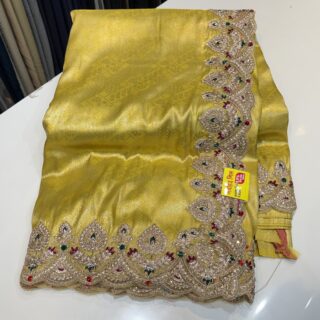 New designer saree #jh110
Original price was: ₹3,700.00.₹2,500.00Current price is: ₹2,500.00.
-
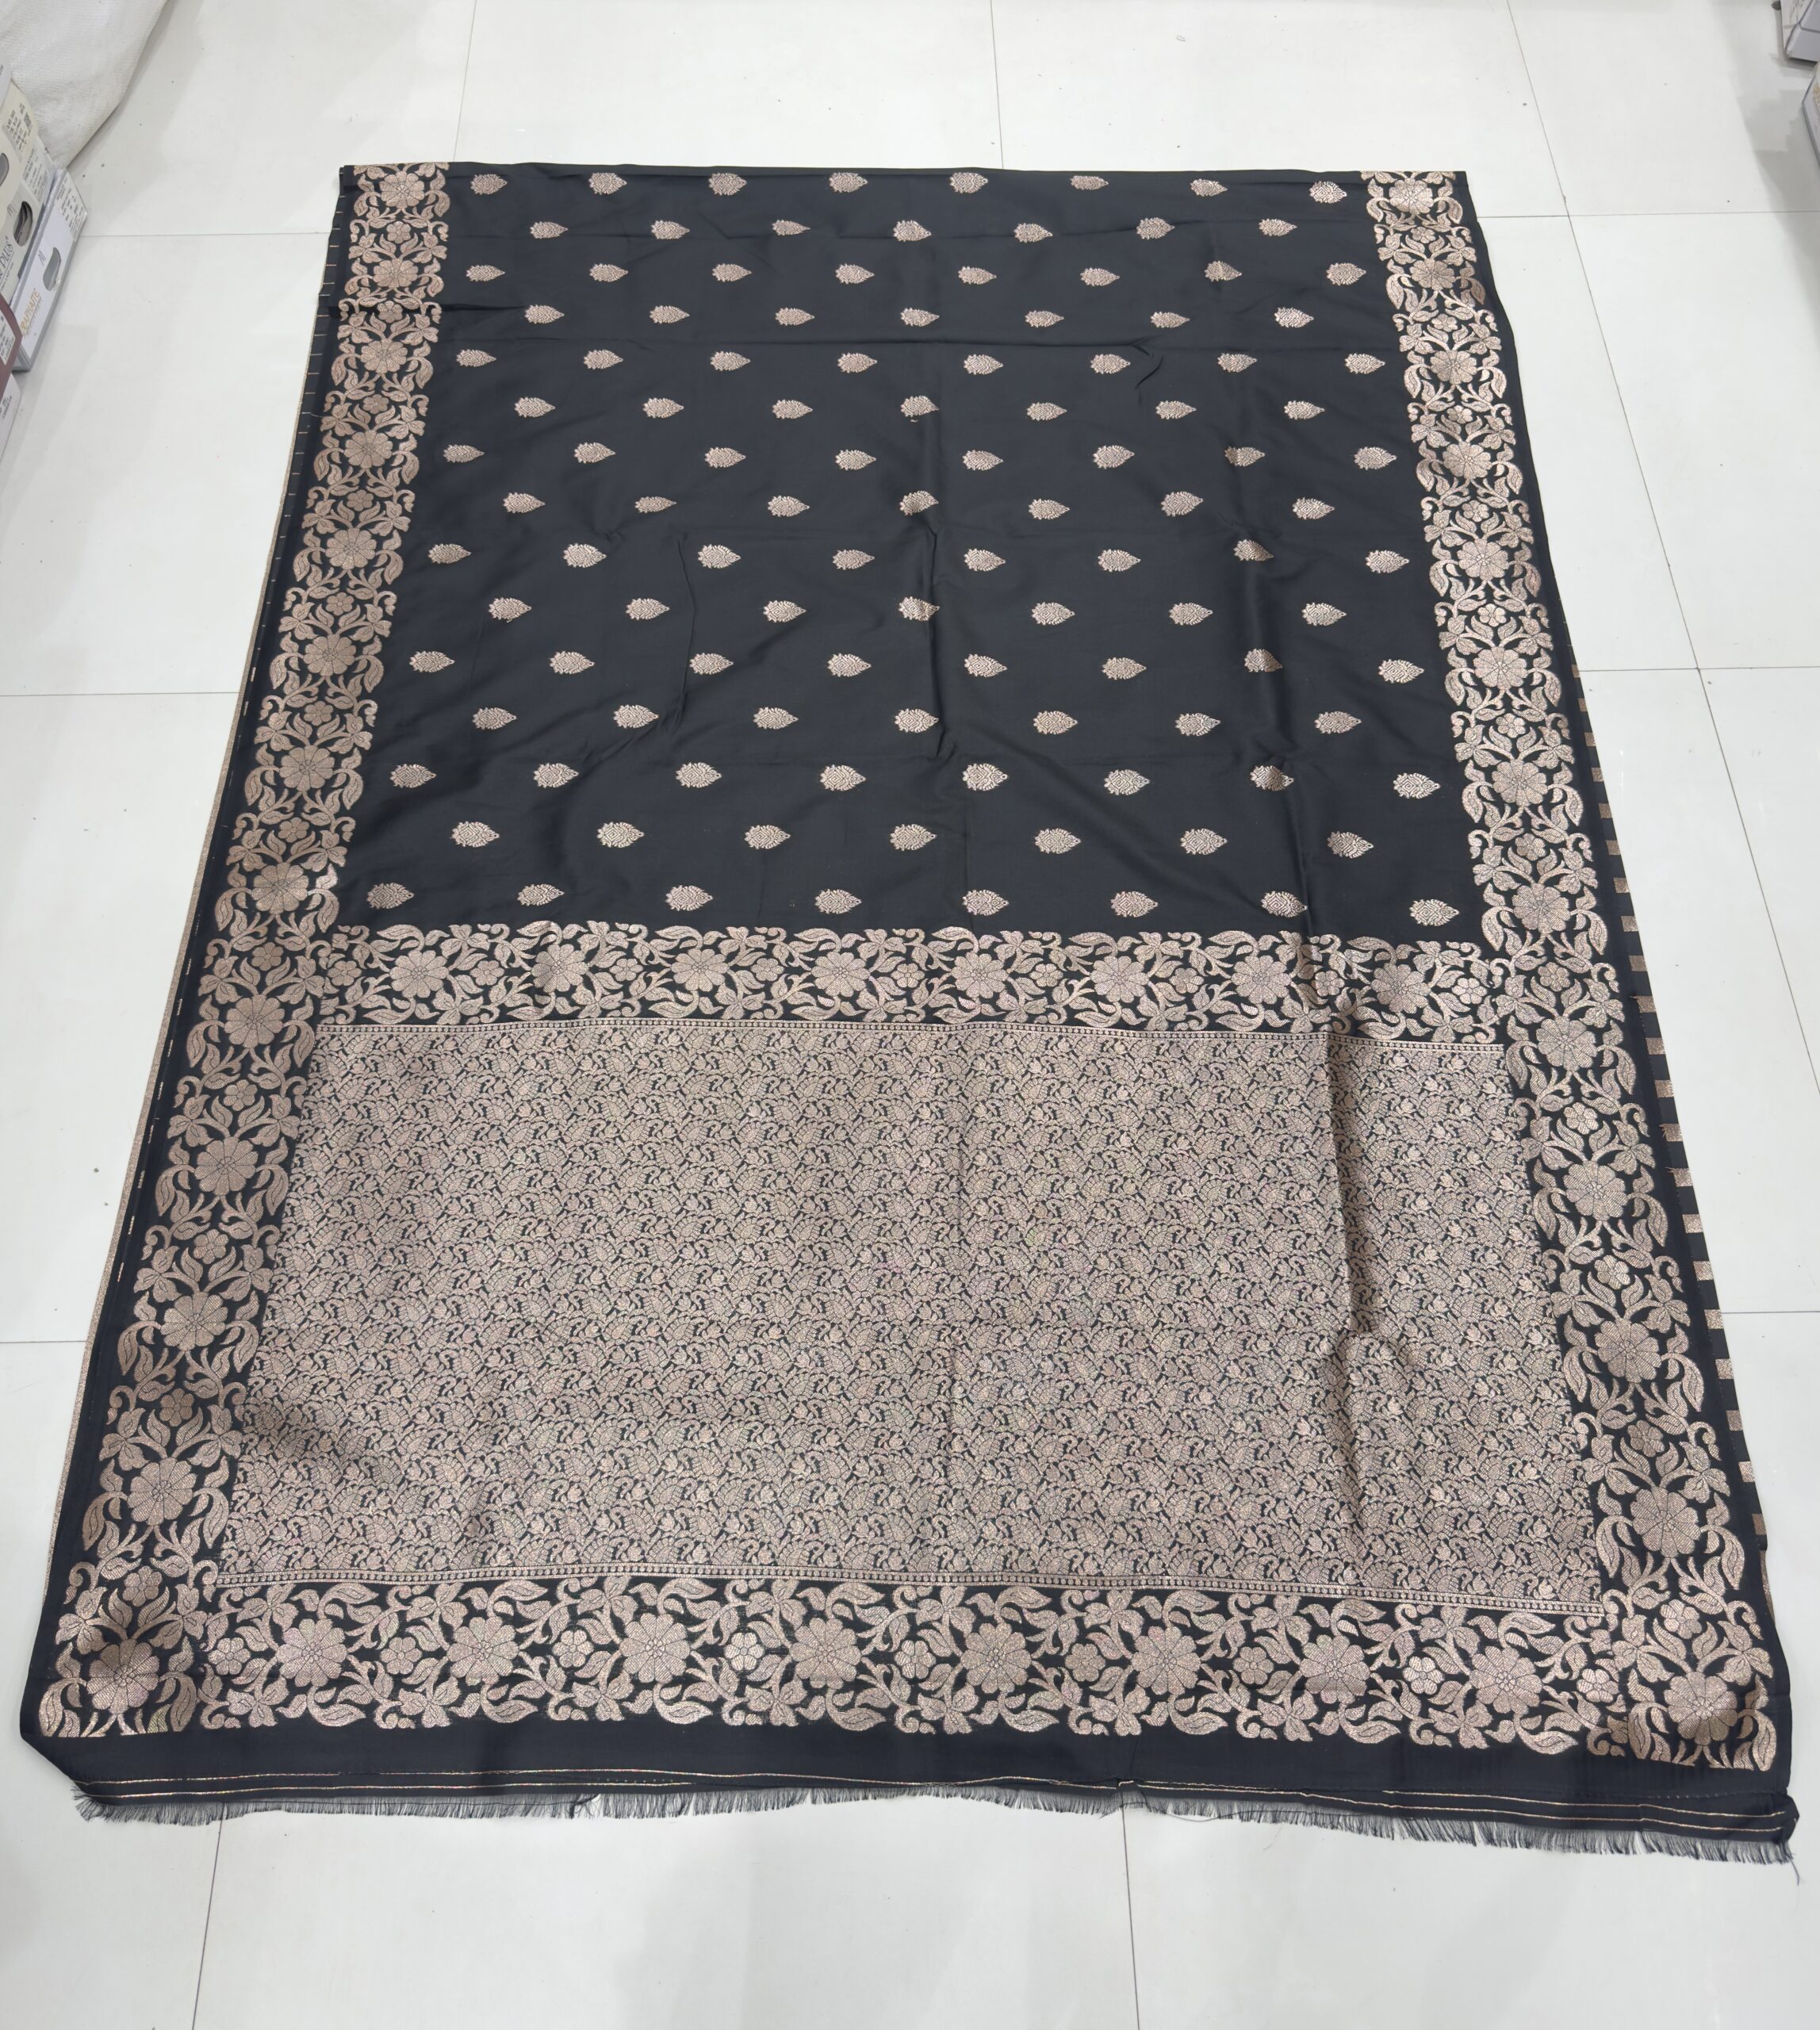
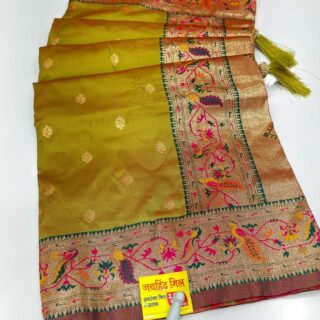 Lotas border saree #jh109
Original price was: ₹1,950.00.₹1,000.00Current price is: ₹1,000.00.
-
 3 pis #jh108
Original price was: ₹1,500.00.₹950.00Current price is: ₹950.00.
GALLERY
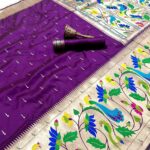
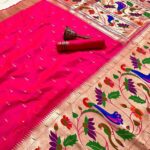
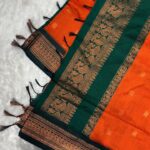
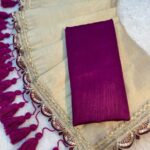
CLIENT'S TESTOMONIAL
Preeti
Amazing collection and great pricing! The designs are unique, and delivery was super fast.
Rohini
Absolutely love the quality of Jai Hind Mills sarees! The fabric is so soft and elegant. Will shop again!

Attackers want to distribute and install their malware, steal your data, and evade detection. Learn everything you need to know about ransomware and how to protect your valuable data from cybercriminals. In this environment, there is no singular, one-size-fits-all approach to preventing Exploits. On one hand, malicious hackers and cybercriminal organizations continually refine their methods to seize control of critical infrastructure, hijack corporate assets, or steal personal data. Companies are placing more weight on building security into the software development process from the ground up.
The directory traversal/path traversal attack (also known as dot dot slash attack) is an HTTP exploit that allows an attacker to access restricted files, directories and commands that reside outside the web server’s root directory. An attacker can then insert a payload that will be included as part of the SQL query and run against the database server. In order to run malicious SQL queries against a database server, an attacker must first find an input within the web application that is included inside an SQL query. https://bestchicago.net/smart-contract-security-audit-service-from-cqr.html Since an SQL Injection vulnerability could possibly affect any website or web application that makes use of an SQL-based database, the vulnerability is one of the oldest, most prevalent and most dangerous of web application vulnerabilities. Protocol vulnerabilities are not immediately identified by vendors or security researchers, so by the time a patch is released, hackers may have already launched a zero-day exploit attack.
- Exploit prevention tools are typically deployed on endpoints and servers, often as part of Endpoint Detection and Response EDR solutions.
- However, in real life, the complexity of software often leaves hackers room to scout for flaws and turn them against the user.
- Protocol vulnerabilities are not immediately identified by vendors or security researchers, so by the time a patch is released, hackers may have already launched a zero-day exploit attack.
- In Client-Side Exploits, the target is the user’s computer or device, typically when they visit a compromised website or open a malicious file.
- Automated patch management solutions can streamline this process, ensuring that you do not overlook critical patches.
Sophos Endpoint utilizes a range of techniques, including credential theft prevention, code cave utilization detection, and APC protection used to gain a presence and remain undetected on victim networks. CryptoGuard uses behavioral analysis to stop previously unseen ransomware and boot record attacks. Vulnerabilities occur in software at an alarming rate, often requiring patches from the vendor – and before those patches, those vulnerabilities remain. With Sophos Endpoint, evasive hackers and zero-day attacks can’t get through – because rather than focusing solely on stopping malware, Sophos Endpoint tracks the behavior that indicates an attack is underway and stops it dead in its tracks. Using a relatively short list of highly effective exploit techniques enables them to do just this.

The essence of exploit prevention
Vulnerabilities are weaknesses that may exist due to poor coding practices, design oversight, misconfigurations, or newly discovered software bugs. At its most basic level, an Exploit is a piece of software code or a method used to take advantage of a vulnerability or flaw in a system, application, or network. We will also delve into examples of famous Exploits, https://travelusanews.com/cqr-is-a-leading-cybersecurity-provider-benefits-of-cooperation.html discussing the massive impact they have had on the cybersecurity landscape.
Conducting regular security audits to target software vulnerabilities
- This helps in creating patches, improving overall system security, and preventing criminals from taking advantage of these weaknesses.
- Network segmentation is done by partitioning a physical network into numerous logical sub-networks.
- In order to detect vulnerabilities and exploit them, hackers must first gain access to the device.
- As technology advances—encompassing artificial intelligence, quantum computing, the Internet of Things (IoT), and more—so too will Exploits.
- In order for an SQL Injection attack to take place, the vulnerable website needs to directly include user input within an SQL statement.
EP provides an efficient and https://indiana-daily.com/smart-contract-security-audit-services-from-cqr-main-advantages.html non-intrusive way for blocking and detection of both known and unknown exploits.
Kaspersky Small Office Security

Often found on compromised websites, they detect a visitor’s system attributes (e.g., browser version, plugins installed) and attempt the most effective Exploit available. Attackers focus on vulnerabilities in common software such as web browsers, media players, or document readers. Because no fix exists at the time of discovery, zero-day Exploits are incredibly dangerous.
- Moreover, exploit prevention applies numerous security mitigation tactics to address the most common attacking techniques used in exploits.
- Attackers often aim to take advantage of weak passwords and gain control over a network and all files in it.
- An attacker can leverage broken algorithms, faulty web app firewalls, poor password security, unprotected open-source components, missing authorizations, and more to perform an SQL injection attack.
- Often found on compromised websites, they detect a visitor’s system attributes (e.g., browser version, plugins installed) and attempt the most effective Exploit available.
- Ransomware is a specific form of malware designed to infect devices and networks to restrict data access until a ransom is paid.
- Once rendered, the content usually causes the application to crash and inadvertently installs a malicious payload without user intervention.

ABOUT US
Jai Hind Mills – A trusted name in premium textiles, blending tradition with innovation to deliver superior quality fabrics.
FEATURED PRODUCTS
AD WIDGET
FROM THE BLOG
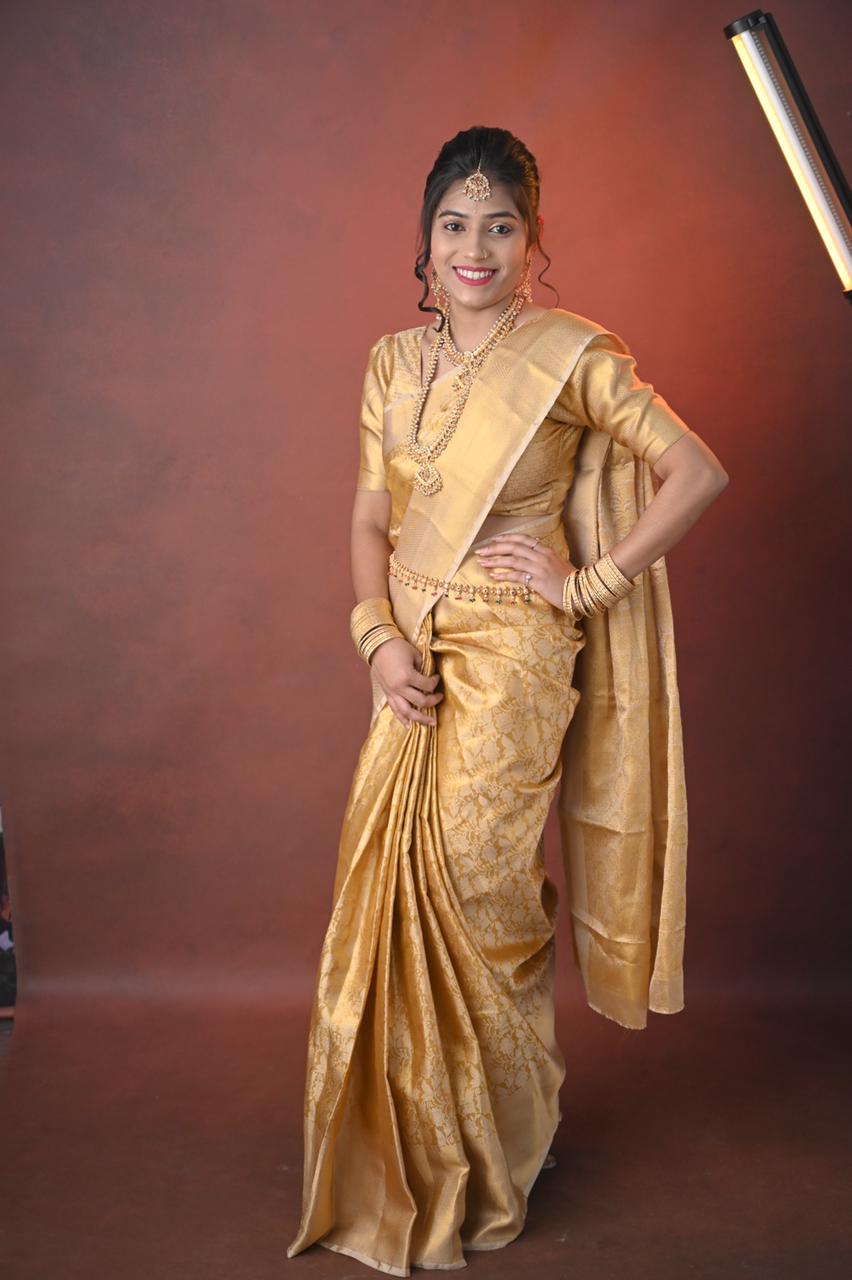
Step into the world of elegance and tradition with Jaihind Mill’s exclusive saree collection. Whether you’re looking for a classic silk saree, a trendy designer drape, or a light and comfortable daily wear, we have something special for every occasion — and now, you can shop it all online! Our saree collection is carefully curated …
Beautiful Saree Collection Now Available Online – Shop at Jaihind MillRead More
Leave a Reply